example.com
A main website name in the three-name list.
Organization validation (OV)
Give a defined set of three domain or subdomain names organization-validated coverage. This option fits an organization that needs verified identity across several eligible addresses and can coordinate their shared certificate lifecycle.
Know the names you are securing
SDH OV Multi-Domain SSL includes three eligible names in the SAN list. The CA verifies the organization and requires proof of control for each name in the request.
A main website name in the three-name list.
Another eligible domain for the verified organization.
An explicitly listed service hostname, using one included name.
Three names are included, not every domain the organization owns. Count required www aliases and subdomains according to the product rules. Additional SANs need a quotation; wildcard coverage is not included.
Match the requirement
Start with the addresses you need to protect and the identity checks your organization requires.
An organization that needs verified identity on three eligible names managed as a single certificate request.
A named group of public or application endpoints where organization validation is a defined requirement.
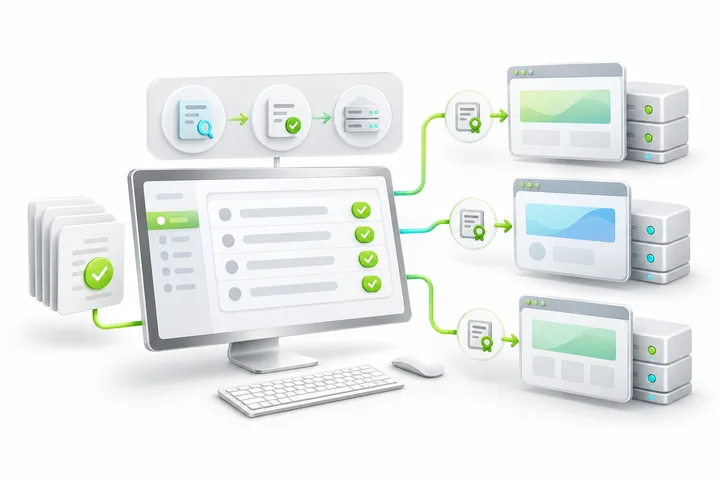
A team able to complete checks for each domain and deploy replacement certificates across all affected services.
HTTPS encrypts data in transit between supported clients and a correctly configured server. It does not guarantee that a website is malware-free or replace secure application and server administration.
Before you begin
Prepare the exact three-name list, organization legal name and a contact for verification. Confirm that every included domain can pass validation and every server can use the resulting certificate.
A CSR is request data, not a private key. Keep private keys, passwords, payment-card details and identity documents out of ordinary website enquiry forms.
A manual process, with clear responsibilities
SDH coordinates your certificate order. The CA performs validation and issuance; your administrator handles installation.
Select the prepaid period for SDH OV Multi-Domain SSL. Review the full upfront total and confirm the names and validation requirements with SDH before proceeding.
Provide a CSR, the complete SAN list and the organization legal name. Resolve alias counting or extra-name requirements with SDH before the certificate request is finalized.
The CA verifies the organization and each requested name. Prepare for additional business information and business-day checks; a blocked domain validation can delay the whole request.
Your administrator installs the issued certificate and chain, configures HTTPS and checks the secured names. Later reissuance can require this step again.
Your selected 1 year prepaid period is paid in full upfront. It does not produce one certificate valid for an unrestricted period. CA and browser rules determine individual certificate validity. Later reissuance, validation and installation may be required within the prepaid subscription.
Understand the purchase
Choose the right certificate coverage and agree any additional technical assistance separately.
Browser and device trust depends on valid issuance, supported clients and correct server configuration. A site seal is available only where the issuer supplies and licenses one for the product.
A new SAN list or server key can trigger a reissue and further validation. Plan changes across all covered services and ask for a quotation before adding names beyond the included three.
Renewal is arranged manually; pricing will be confirmed before renewal. Reissuance is subject to the issuer's rules and does not include SDH installation labor or promise that every name change is free.
Frequently asked questions
Prepare the organization details and all three names. Each requested name needs domain-control validation.
No. Organization validation establishes identity; the SAN list determines name coverage. This package includes three eligible names and requires domain-control checks for them.
Yes, aliases and subdomains can use the available names according to the actual product rules. Send the exact list so coverage can be confirmed instead of assuming extra aliases are included.
A wildcard can fit eligible first-level subdomains beneath one base domain. Multi-domain coverage is useful for explicit names across different eligible domains. Match the actual hostname list before deciding.
No. The certificate purchase does not include installation, server repair, mixed-content fixes or continuous certificate management. Your hosting administrator installs and verifies the certificate; ask SDH about separately agreed assistance if needed.
No. The prepaid term is the purchased subscription period. Individual certificate validity is subject to CA and browser requirements, so you may need reissuance, validation and replacement installation during that period.
Renewal is arranged manually; pricing will be confirmed before renewal. New validation and issuance steps may be needed. The current prepaid price is not a promise of future renewal pricing or automatic renewal.
Compare the alternatives
Keep OV with simpler single-domain coverage.
Explore this certificate
Keep three-name coverage and request extended validation.
Explore this certificate
Use OV for eligible first-level subdomains of one base domain.
Explore this certificateTell SDH what you need to secure. Include public hostnames and a short overview of the requirement.